New capability identifies, attributes and validates API keys, OAuth tokens and other machine credentials stolen from developer and employee endpoints
BNEI BRAK, Israel, Aug. 31, 2026 (GLOBE NEWSWIRE) — Lunar Cyber today announced Token Exposure Monitoring, a new capability designed to identify, attribute and validate Non-Human Identities (NHI) and machine credentials inside infostealer logs, connect them to the affected organization, and determine which exposures require action.
The rapid adoption of AI development tools, cloud platforms and automated infrastructure has put a new class of credentials on developer machines: API keys, OAuth tokens, personal access tokens, and other machine identities that provide direct access to valuable services.
Security researchers have documented the theft and abuse of AI API credentials for attacks such as LLMjacking, where stolen keys are used to run expensive AI workloads through a victim’s account. Developer credentials can also provide access to source-code repositories, cloud infrastructure, SaaS platforms and corporate data. Lunar’s internal research found that modern infostealers actively collect the local files and application data where these credentials are frequently stored.
Developers routinely authenticate to services such as AWS, GitHub, OpenAI, Anthropic, Slack, Okta and other cloud and development platforms from their workstations. Tokens can be stored in .env files, application configuration, CLI authentication files, shell history, browser data and local caches. Modern infostealers use file-grabber components to collect exactly this type of endpoint data.
The growing use of AI development tools has expanded that exposure. Persistent API and OAuth credentials are increasingly used by AI APIs, command-line agents and developer environments, placing valuable machine credentials directly on endpoints targeted by malware.
“Developer tokens have become valuable credentials in their own right,” said Ran Geva, Founder and CEO of Webz.io. “A stolen AI key can be converted into compute almost immediately. A GitHub token can provide access to source code, and a cloud credential can open infrastructure. Security teams need visibility into these credentials at the moment they appear in an infostealer log, with enough context to understand who they belong to and what needs to be revoked.”
From an Anonymous Token to an Actionable Incident
Machine credentials create a different intelligence problem from traditional compromised passwords. An exposed corporate email address carries its organizational identity inside the credential. An API token generally appears as an opaque string with little indication of who owns it.
Lunar analyzes the surrounding infostealer data to solve that attribution problem. The platform associates exposed secrets with the compromised employee or organizational endpoint, identifies the service and credential type, and retains forensic evidence showing where the secret appeared.
For supported credentials, Lunar also checks their validation state. Analysts can distinguish between findings based on service, credential type, severity and validation status rather than treating every token-like string as an equivalent alert.
The Token Exposure interface provides access to the exposed credential, affected employee, service, internal file path, original log context, malware metadata and other information collected from the compromised endpoint. Analysts can search and filter exposures by service, employee, token type, breach date, severity and validation state.

Extending infostealer response beyond passwords and sessions
Most infostealer response processes center on cleaning the infected endpoint, resetting passwords and invalidating browser sessions. Machine credentials introduce another remediation path because API keys, PATs, OAuth tokens and other secrets frequently follow independent authentication lifecycles and can remain usable until they are rotated or revoked.
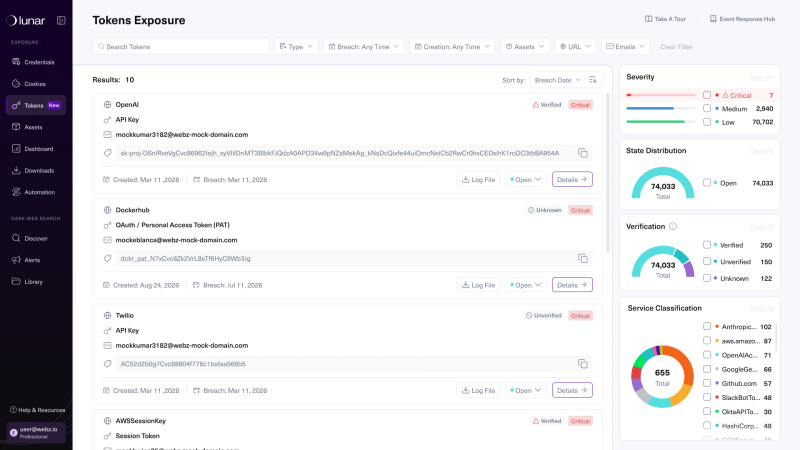
Lunar Token Exposure Monitoring adds machine credential discovery to that response process. Once an affected token is identified, security teams can rotate or revoke the credential and investigate activity within the corresponding service.
The capability complements repository secret scanning, secrets management and NHI security products. Those systems help organizations control machine identities internally, while Lunar provides intelligence about credentials that have already been extracted from an endpoint by malware.
“Passwords and cookies have been at the center of infostealer response for years,” Geva said. “Developer tokens now deserve the same treatment. If the malware took the credential, the incident response process needs to find it, validate it and rotate it.”
Token Exposure Monitoring is available in Lunar Essential & PRO Tiers.
About Lunar Cyber
Lunar Cyber provides compromised-credential intelligence that helps organizations identify and investigate employee exposure originating from data breaches and infostealer malware. Lunar combines Webz.io’s collection infrastructure with forensic context, validation and response workflows to help security teams identify compromised access and respond quickly.
For more information, users can visit lunarcyber.com.
Contact
CEO
Ran Geva
Webz.io LTD
[email protected]
Photos accompanying this announcement are available at:
https://www.globenewswire.com/NewsRoom/AttachmentNg/3679f292-ef5a-446b-9d85-622148a6664e
https://www.globenewswire.com/NewsRoom/AttachmentNg/0f2c10cf-105c-4d54-a064-5729ad4163f5
https://www.globenewswire.com/NewsRoom/AttachmentNg/e177d2dc-6589-40eb-a890-3c54793be63d
